
USB drives are convenient for moving files between computers, backing up records, or carrying documents on the road, but that portability also makes them easy to lose or steal. If a drive with sensitive data ends up in the wrong hands, encryption is what keeps that data unreadable without proper authentication.
Kingston Technology has outlined four criteria it says buyers should check before trusting a drive labeled “encrypted.”
- A manufacturer with a track record. Kingston recommends sticking to vendors with real experience in secure storage, ones whose products have gone through independent testing, including penetration testing. Price and capacity aren’t reliable indicators of actual security, and neither is generic “encryption” marketing language.
- Hardware-based encryption that’s always on. Software encryption can be undermined by malware or other software-level attacks. Hardware-encrypted drives instead use a dedicated secure microprocessor: files are encrypted automatically when saved and only decrypted after authentication. Kingston points to XTS-AES 256-bit hardware encryption specifically, which keeps encryption keys inside the device and doesn’t let users turn protection off.
- Recognized certifications. For organizations handling sensitive data, Kingston says to look for standards like NIST FIPS 140-3, the US government encryption standard that requires independent testing, and TAA compliance, which matters for US federal and defense procurement. Both are third-party validation that a product’s security claims actually hold up.
- Extra protection layers beyond encryption itself. This includes brute-force protection that wipes the drive after repeated failed password attempts, BadUSB protection against firmware tampering, multiple password tiers for admin/user access or recovery, and read-only modes to prevent tampering when the drive is plugged into an untrusted machine.
Which Drive for Which Use Case
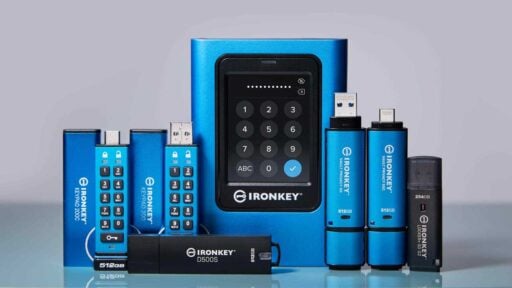
Kingston’s IronKey lineup covers a range of use cases:
- Everyday users, students, and families — IronKey Locker+ 50 G2 offers XTS-AES 256-bit hardware encryption with a multi-password option and no software installation required.
- Freelancers and remote workers — IronKey Vault Privacy 50 adds Admin, User, and One-Time Recovery password options on top of the same hardware encryption.
- Professionals on specialized/regulated equipment — IronKey Keypad 200 is FIPS 140-3 Level 3 validated and uses an alphanumeric keypad for PIN-based, OS-independent unlocking, plus tamper-resistant construction.
- Small and medium businesses — IronKey Vault Privacy 80 External SSD goes up to 8TB with a touchscreen interface, and has picked up multiple ASTORS Homeland Security Awards.
- Regulated industries (finance, healthcare, legal, government) — IronKey D500S is FIPS 140-3 Level 3 validated, TAA-compliant, built to MIL-STD-810F, and uses a rugged zinc casing with epoxy-filled construction and automated crypto-erase.
Kingston’s IronKey drives also carry FIPS 197 certification alongside the FIPS 140-3 Level 3 validation and TAA compliance noted above.